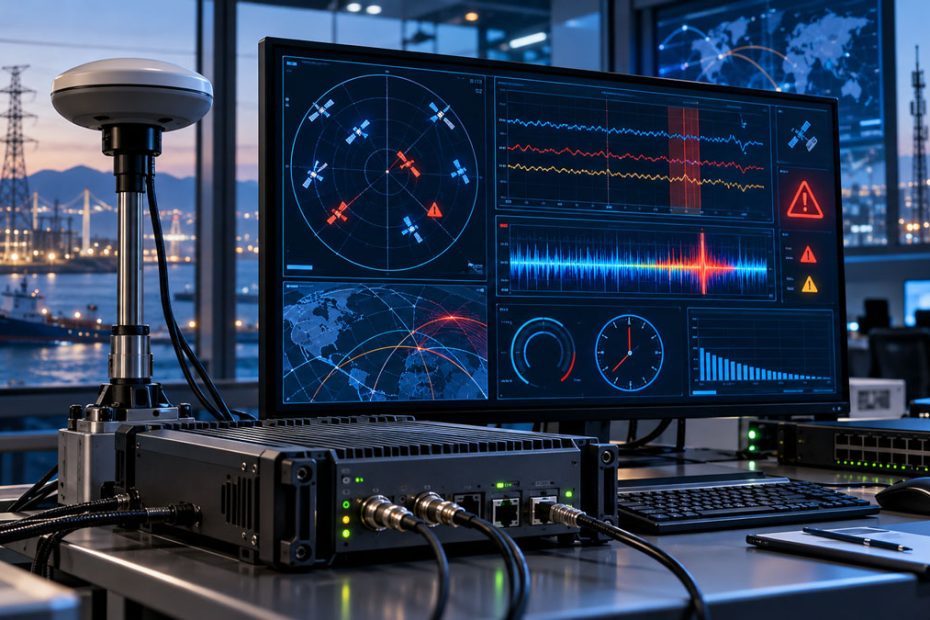
CyberPrism has launched CyberPrism Canary, a new monitoring system designed to detect when Global Navigation Satellite System data may have become unreliable because of spoofing, jamming or other forms of signal disruption. Rather than attempting to maintain a navigation or timing output during an interference event, Canary is built to answer a more fundamental question: can the GNSS-derived data still be trusted?
The system continuously compares time obtained from its integrated GNSS receiver with independently sourced Network Time Protocol data. A growing discrepancy between those references can indicate that the satellite-derived source is being disrupted or manipulated, allowing operators to treat associated positioning, navigation and timing information with greater caution.
CyberPrism describes Canary as a detection and alerting platform rather than a technology that prevents GNSS interference. The system is aimed primarily at operational technology environments where incorrect position or timing information can affect industrial processes, electrical infrastructure, telecommunications, maritime operations and other critical systems.
GNSS and NTP Cross-Checking
The underlying principle is relatively straightforward. GNSS receivers obtain highly accurate time from satellite navigation constellations such as GPS, Galileo, GLONASS and BeiDou, and that timing information is widely used for synchronizing communications networks, industrial equipment, electrical systems and distributed monitoring infrastructure.
CyberPrism Canary introduces a second reference through multiple external NTP sources and continuously compares that network-derived time against the GNSS clock. Under normal conditions, the two references should remain within an expected tolerance. If GNSS time begins moving away from the independent reference, the system can identify the discrepancy as an indication that the satellite-derived source may no longer be trustworthy.
This approach is particularly relevant to spoofing because a sophisticated spoofing transmitter can generate counterfeit satellite signals that cause a GNSS receiver to calculate an incorrect position or time while continuing to operate apparently normally. The receiver may still report a valid fix, an adequate number of satellites and plausible navigation data even though the underlying solution has already been corrupted.
Spoofing and Jamming Detection
Jamming and spoofing affect GNSS receivers in different ways. Jamming introduces radio-frequency interference into GNSS bands, reducing the receiver’s ability to acquire or track legitimate satellite signals. Depending on the strength and characteristics of the interference, the result can range from degraded accuracy and reduced satellite availability to complete loss of positioning.
Spoofing is potentially more difficult to recognize because counterfeit signals are used to manipulate the calculated solution rather than simply preventing reception. Instead of losing its position fix, a receiver may continue producing convincing but incorrect position or timing data, creating a greater risk that downstream systems will accept false information as valid.
CyberPrism Canary monitors several indicators associated with this type of degradation, including GNSS data quality, device health, timing accuracy, signal loss, malformed messages, timing drift and discrepancies between GNSS and NTP references. The system can then generate high-visibility alerts when predefined abnormalities are detected.
Importantly, CyberPrism does not claim that Canary prevents spoofing or jamming. Its role is to provide an independent indication that GNSS information should no longer be accepted at face value, giving operators an opportunity to move to alternative procedures or sources before unreliable data affects critical operations.
GNSS Timing in Critical Infrastructure
GNSS is frequently associated with vehicle navigation, but precise timing is one of its most important infrastructure applications. Electrical grids, telecommunications networks, financial systems, industrial control systems and distributed monitoring equipment can all depend on synchronized clocks, often with much tighter tolerances than are visible to end users.
In an electrical network, precise timestamps may be required for event sequencing, fault monitoring, switching operations and synchronization between geographically separated assets. If different devices begin operating from inconsistent time references, diagnosing faults or coordinating systems becomes more difficult and, in some applications, potentially unsafe.
Similar problems can arise in industrial control environments where logs from PLCs, controllers, sensors, security systems and network devices need to be correlated accurately. If timestamps drift apart, engineers may have difficulty determining the true sequence of events during a failure or cybersecurity incident.
CyberPrism says that the UK National PNT Office estimates 97% of UK Critical National Infrastructure depends on GNSS services in some form. The company also cites a UK government study estimating that GNSS contributes more than £13.6 billion annually to the UK economy, while a seven-day disruption could produce an economic impact of around £7.6 billion.
GNSS Interference Is Increasing
The launch of Canary comes as GNSS interference has become a much more visible operational problem. CyberPrism cites European Space Agency figures indicating that more than 10,000 vessels were affected by malicious GNSS interference during a single quarter of 2025, approximately eight times the number recorded in the previous quarter.
The company also references FAA and EASA data covering roughly 150,000 GPS loss events across five million flight operations over a 12-month period. Aviation and maritime incidents have drawn particular attention because navigation errors are immediately visible, but similar interference can affect any system that depends on satellite-derived positioning or timing.
The distinction between complete signal loss and corrupted data is important. A system that clearly stops producing navigation information can trigger established fallback procedures. A receiver that continues supplying believable but incorrect information creates a more difficult operational risk because operators and connected systems may have no immediate reason to distrust the output.
OT Alarm Integration
Canary has been designed specifically for operational technology installations rather than only conventional IT environments. One of its practical features is support for VFC, or volt-free contact, integration, allowing the monitoring system to connect to existing industrial alarm equipment without requiring a complex software interface.
A detected event could therefore trigger an external warning light, audible alarm, relay input or another predefined operational response. This is relevant in industrial facilities where critical alerts cannot depend entirely on an operator continuously watching a software dashboard.
The platform also combines GNSS signals, timing information, device state and system status into a unified interface intended to give operators a single operational view. CyberPrism says the alarm engine continuously monitors data quality, device health and timing accuracy while generating alerts for conditions such as signal loss, malformed messages and timing drift.
Logging GNSS Incidents
CyberPrism has also placed significant emphasis on event logging. Canary incorporates a high-performance log-rotation system designed to retain evidence while controlling storage requirements, with logs available for incident investigation, auditing and post-event analysis.
That capability could be particularly useful because many interference events are temporary. By the time engineers begin investigating a navigation or synchronization problem, the original radio-frequency conditions may have disappeared. Historical timing differences, receiver states, alarms and message errors can help establish when an event began, how long it lasted and how connected systems responded.
The architecture is described as modular, with support for multiple signal types, power configurations and logging methods. This should make it easier to integrate Canary into different operational environments rather than treating it as a single fixed-purpose appliance.
Why Canary Is Different
The most interesting aspect of Canary is that CyberPrism is not trying to claim that it can make satellite signals immune to interference. That distinction is technically important because anti-jam antennas, controlled reception pattern antennas, multi-frequency receivers, inertial navigation systems and sensor-fusion platforms can improve resilience, but none of them changes the fundamental fact that GNSS signals reaching the Earth’s surface are extremely weak and vulnerable to disruption.
CyberPrism is instead introducing a separate integrity-monitoring layer. From a system architecture perspective, that is valuable because availability and integrity are not the same problem. A navigation or timing system may remain operational while the integrity of its data has already been compromised.
Canary’s clock-comparison approach provides an external reference that may expose that condition. It does not replace anti-jamming hardware, inertial systems or redundant positioning sources, but it can add another layer of evidence when operators need to decide whether GNSS-derived information should still be trusted.
The NTP Question
There is, however, an important technical limitation that deserves attention. The value of any NTP comparison depends heavily on how independent and trustworthy those NTP references actually are. If an external time server ultimately derives its own time from the same GNSS source, or if the network time path can itself be manipulated, the independence of the comparison is reduced.
For critical infrastructure deployments, this means the strongest implementations will require carefully selected and preferably diverse time references rather than treating any internet-accessible NTP server as an authoritative source. A combination of independent timing technologies, disciplined oscillators, terrestrial references and multiple GNSS or network sources can provide a more robust integrity model.
That limitation does not weaken Canary’s basic concept. It highlights the broader engineering principle behind it: GNSS integrity monitoring becomes more useful when several technologies with different failure mechanisms are compared against one another.
Integrity Over Continuity
Canary also reflects a broader change in how resilient positioning and timing systems are being evaluated. Keeping an output alive is not necessarily the same as maintaining a trustworthy solution.
A receiver can bridge an outage using an oscillator, inertial measurement unit, wheel sensors, dead reckoning or calculated trajectory. Those techniques can be extremely useful for maintaining operations, but the resulting solution should not automatically be interpreted as live, uncompromised GNSS data.
For safety-critical and operational technology applications, knowing the confidence level of the underlying information can sometimes be more important than simply maintaining an uninterrupted position or timing output. CyberPrism Canary approaches that problem from the monitoring side, providing another mechanism for identifying when operators should stop treating GNSS as authoritative.
For electrical networks, maritime infrastructure, telecommunications and other systems built around precise positioning or synchronization, that distinction may ultimately be more important than the relatively simple two-clock principle suggests.
About CyberPrism
CyberPrism is a UK operational technology cybersecurity company focused on Critical National Infrastructure, industrial networks, energy, maritime, utilities, manufacturing and defense applications. Cyber Prism Limited was incorporated on October 19, 2016, and remains an active UK private limited company under registration number 10436037.
The company describes itself as an NCSC Assured Cyber Security Consultancy dedicated to Operational Technology and operates in the UK and international markets. Its portfolio includes CyberPrism Canary, CyberPrism Assure, CyberPrism Guard and OT cybersecurity consulting services.
CyberPrism’s leadership includes Managing Director Martin Smith, a former Commandant General of the Royal Marines with 33 years of maritime security and military information experience, and Technical Director Keith Chappell, who has more than 30 years of IT and OT experience, including work with Critical National Infrastructure, offshore facilities and shipping.
The company reported in December 2024 that its staffing footprint had increased by 60% following contract awards from four North Sea operators. LinkedIn currently places CyberPrism in the 11 to 50 employee company-size category.